Tuesday, April 16, 2013

Ihack2013 - Forensic Writeup Challenge 300 Point - VM Forensic

As requested by Mr Ramadhan, here's the writeup!
The question was
So each team was given with this file 695f616d5f7468655f6861786f72.7z.
Extract it will gives them another folder and in it there's a file named ihaxor.
What kind of file is that? Again, use FILE command.
Yes. Its a tar archive. Extract it again will give you a virtualbox image. Import it in your virtualbox machine.

Hello Slitaz! Its a slitaz VM. Dont know the password? Please,google it.

Ok now I'm in. What's next? Most of the teams were confused with the files exist in this slitaz. Everyone keep thinking the way to be a root user..But its not the right way to solve it! Why those folders existed? Yeah, of course I put it as a troll LOL!

Read the question "Dont think too hard". As a Pro Hacker, please..a basic step. Look for ALL files available first.

Yeah. There's a .ash_history  file. Look at that file. Its a common thing once you get into someone's PC in order to do some forensic investigation.
Viewed the file and will noticed that there's a weird file named wipipipipi.txt. Did you guys try to look for that file??
Woot!! I found the file. Its in the /log folder. (and its one of the folder that a forensic investigator should look at )
Found,lets look what is inside.
TADAAAAAA!!! there's your flag!
flag is f0r3ns!c.is.3asy

muahahahaha..easy right?! Trolled hard?yeah you got trolled. Stop claiming yourself as a hacker now. LOL

Monday, April 15, 2013

Ihack2013 - Forensic Writeup Challenge 100 Point - Image Analysis

Here's the 2nd one for Forensic Challenge 100 points. People keep up trying on this one..seems there's no one can answer this during the game..so unlucky :P
If you guys look back at the previous Ihack 2010 by Yondie, there's a similar puzzle given in Hack&Defence category.

Let's look at the writeup!
Team were given with this Kamen Rider GIF file.

If you guys look at the file carefully. There are several images with same design.YERP! the one with kamen rider + their airing years :P
Extract them and eliminate those that are not related.
Then?
Did you guys read the question carefully?again..there's already a CLUE in it!!
"you should start watching them"
when we'r going to watch a series, we should watch starting from the first one. So, put the kamen rider in order based on their airing years.
Some of the contestants already manage until this part,but then they dont know what to do.hahaha..
Here's the way to get the flag.
For each images extracted, look at the COLORS!

- Open up your photo editor such as GIMP or Photoshop.
- Use Color Picker Tool.
- Click on the Font's color.
- Look at the color's code!!

By put the code in order,you'll get the hex code,decode it you'll get the flag :P


muahahahahahaha :P

Ihack2013 - Forensic Writeup Challenge 100 Point - Cryptography

Ihack2013 already finished but most of the contestants still eager to know what's the solution for most of the questions.
Here's 1 of them.

They were given a file with this image as a clue.

A clue?!! yes..each image for every questions is THE CLUE!
So what's the relation between Ash Ketchum from Pokemon with this cryptography?

 Wait.How did I know that file is an image file? Basic forensic step. Use FILE command in linux to identify the type of that file.

So I can see some of the contestants using many ways to decode the code. Applause to them. Its great to see some efforts from the youngsters :D

So what's actually this code is about? And the important thing is,WTF IS THIS CODE?!!
Its a bionicle encoding.
Google about them :)

Then,WHY THE HELL THERE ARE LOTS OF POKEBALLS?!!
Hard to decode it 1 by 1? Here's the trick, you just need to decode the 1st line of the cryptography message. Once you decoded it, try to google them.
Yes! The code is coming from Pokemon's wikipedia which already mentioned by the clue!
So encode the paragraph where your 1st line decoded message were using online bionicle encoding tool, compare it with the question given by the forensic game, you'll notice a slightly difference in the coded message. Yes there's where the flag located. Decode that part and voilla. You got the flag!
Flag is g0tta.h4cK.th3m.@LL

Its not hard at all :P
Congratz for those manage to get the flag.

Thursday, April 11, 2013

How I Rewarded with USD?K Just With a Simple Search Form

Hello.
Its been a while and I'm quite busy with works lately. Today I want to share with you guys on my recent successful findings on Paypal Bug Bounty Program.

Paypal's Bug Bounty Program currently limited its testing application so in order for you to find any bug quite hard nowdays. Read it here from ehackingnews

One of the Apps that still under the scope is BillSafe. Previously, I noticed that @Vigneshkumarmr found XSS and CSRF in that application however he was not the one the 1st person found it. @KrutarthShukla was the one that rewarded by Paypal for his submissions on Billsafe.


Then that day I just trying my luck to see if there's any bug that was missed by other researchers/hunters. Looking around..hmm..no luck..until..I met this search form

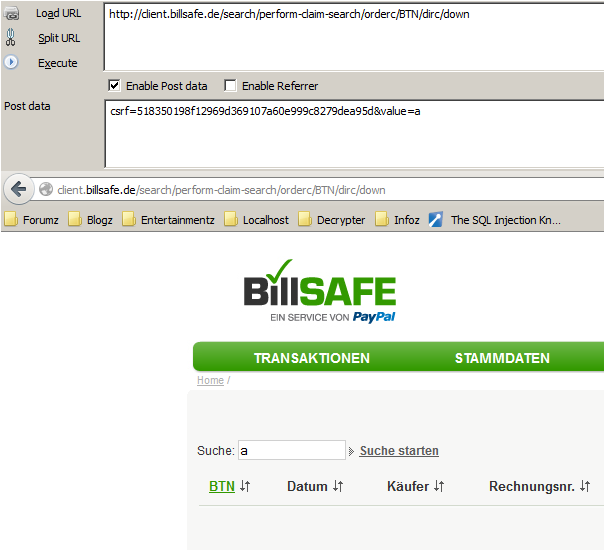
Its a search form where we can see our transaction history. I tried to search some random words. Nothing unusual.


Then with the power of double quotes, BOOM! The page become blank!
Aha! Now its weird. At first I thought it might be just a normal error. So I tried to close the double quotes.
BAM!! Welcome to papa Blind SQLi!
And it will be not enough with just like that. I need to give them a working POC. Tried to use a common technique. Not working..darn!..I take a look..have a rest..take my coffee..then suddenly..my brain knocked on me " lets try with a simple sql query "

So I tried using something like “ or column_name like “%
How it'll working? Simple. If the column_name I guess is TRUE, the page will load normally..else it'll become blank. So does it works?
OF COURSE!


and is it done? Yes.For SQLi. As a bonus, I found that this form is vulnerable to XSS as well.

All of these bugs had been fixed by Paypal. And I already received the payment. How much? I leave it to your imagination.

ADIOS!

@yappare.

Sunday, March 24, 2013

Cisco T-Shirt

Hi! Remember the SQLi bug I found in Cisco website previously?
Here's what I received from them as a token of appreciation!


Tuesday, March 5, 2013

SQLi in Cisco.com


Its been a while.
Nothing much going to bubbling here :/
Just want to share with you guys with my recent finding on Cisco. There's a SQLi bug in one of their application.

The bug exist at the forgotpassword page in one of their public application which I bet quite important.The parameter affected is UserName

The error appear once we put a single quote (')

We can use Blind SQLi Technique on this. :)


Disclosure :
Found date                 - 19/12/2012
Reported date             - 20/12/2012
Vendor responded but no news after 31/12/2012 (busy with holiday?)
Again reported            - 18/02/2013
CSIRT Team replied   - 19/02/2013
Bug fixed                    - 01/03/2013
Public disclosure         - 06/03/2013

Monday, February 18, 2013

Blind SQLi Detection and How to Inject it

Hello all,

So, today I want to share with you guys on how to detect if the website is vulnerable to Blind SQLi or not.
Before, do note that I'm not an expert in this security/hacking scene. This sharing based on my own understanding from articles/discussions among of these great people

  • Mario Heiderich
  • Miroslav Stampar 
  • R4x0r4x
  • Nurfed
  • Reiners
  • benzi
  • and more :)
In this article, I'll use OWASP Broken Web Applications Project as example. You guys can get it Here. Hope you guys already have a basic in SQLi so this wont be hard on you guys :
Ok lets move on.
In Blind SQLi, we need to understand correctly on how the server/website response based on TRUE or FALSE condition.There are 2 ways (afaik based on my knowledge) to detect it.

  1. Quotes
It can be either single quote (') , double quotes (")  or backtick ( ` )
Refer example below.


A normal page condition ( TRUE condition )

The page become blank (FALSE condition) once we put a single quote

The page back to normal condition (TRUE) once we put another single quote.
We can use these method as well to check the TRUE/FALSE condition under this way of detection.

    2. Numeric Operators
 Use a simple math! Check the example shown below where pic_id is vulnerable to SQLi

Normal page loaded. Because the condition is true. 1=1 is TRUE

The admin word is missing. This shows a FALSE condition since 1=2 is FALSE.
Another way is by using simple calculation. The current page loaded fine on pic_id=13.

The page loaded fine but it shows another page. This is because we added 1 in the pic_id where it'll become 13+1=14 so the page will loaded the pic_id=14

Here are some other method under this technique.

So, how are we going to proceed with our Blind SQLi?
Each dbms have a different techniques but quite similar. In this article, I'll show some common technique used in MySQL dbms.

i. Common technique
id=1 and 1=1
id=1 and (put our sql query here)=(put our expectation here)
as  example we want to query the current version,
id=1 and substring(@@version,1,1)=4
so, if the current MySQL version used by the website started with 4 the page will load fine (TRUE condition) else the page will be error/blank (FALSE condition)

Example shown below.
Testing if the MySQL used is version 4.*. Page error,shows that the website is not using that version.

Testing if the MySQL used is version 5.*. Page loaded fine,shows the current version used is 5.*


ii. Using a Case statement
id=1 and 1
id=1 and (CASE when (our sql query here) THEN 1 else 0 END)
If the query is TRUE,it'll resulting 1 where 1 is TRUE condition. Else, it'll resulting 0 where 0 is FALSE condition.

1=2 is wrong,so it'll resulting 0,FALSE.
1=1 is correct,so it'll resulting 1,TRUE.

iii. Time Based
Yup,this is another technique of Blind SQLi based on the server time response.
This technique already explained in my previous post here

and there are more techniques in SQLi out there. Do have some read and research on them as well. You might find a new way on exploiting, who knows right? :D

That's all guys! Hope this article can help you guys a little bit. I'm sorry if the article is not meet your expectation. Tried my best! -__-"

Thanks,
@yappare


Sunday, February 17, 2013

Shit Bypasser

Tired with those short URL when downloading part by part?!
Here's a nice bypasser made by Shahril and Munajaf from Tbd.my


<?php
/*
* Rebuild by Shahril and Munajaf
* Learning Regex trololololo
* Coded By Shahril 
* Styled, Cut,Paste every random shit by Munajaf
* Some Shit From http://pastebin.com/7aE0ZCYk
*
* 1.0 - adf.ly,q.gs,linkbucks,tinybucks,urlcash,lix.in,anonym.to, adik beradik goo.gl pn bole!
*     - Example1 : http://lix.in/-ceec7a
*       - Example2 : http://goo.gl/e4SPw
*
* 1.1 - added anonymz.com,adfoc.us some bug fix
*     - http://adfoc.us/x19219978
*     - http://www.anonymz.com/?http://google.com/
*
*
* 1.0 - 15/2/2013
* 1.1 - 17/2/2013
*
* 
*/

$CounT = true; //set this to true if you want it to count the link have been skiped, " else " put it false
if(!file_exists('link.txt'))
{
    fwrite(fopen('link.txt','w'), "0");
}

if(!in_array("curl", @get_loaded_extensions()))
{
    die('Curl Is Not Supported!');
}

?>
<title>Random Shit Bypasser 1.1</title>
<style>
@import url(http://fonts.googleapis.com/css?family=Fredoka+One);@import url(http://fonts.googleapis.com/css?family=Alike);
body {background:url('http://goo.gl/ZHzmP'); font: 75%/170% Arial, Helvetica, sans-serif;}
a:visited {COLOR: #0066cc;text-decoration: none;cursor:pointer;}
a:link {COLOR: rgb(6, 118, 146);text-decoration: none;cursor:pointer;}
textarea{font-family: 'Fredoka One', cursive;font-weight:200;font-size: 14px;padding:5px;box-shadow: rgba(255, 255, 255, .75) 0px 0px 9px 1px;background-color:rgba(0, 0, 0, .25);    color: rgb(6, 118, 146);;border-radius:5px;height: 198px; width: 887px;margin-top: 20px;margin-bottom: 5px;}
.link{font-size:12px;}
.shittendstohappen{font-size:12px; color:red}
.head{color: #FFF;font-family: 'Fredoka One', cursive;font-size: 50px;font-weight:400;}
.foot{font-family: 'Fredoka One', cursive;padding: 2px;border-top: 1px solid #EBEBEB;background-color: #FFF;bottom:0;position:fixed;width:100%;height: 20px;font-size: 15px;}
.number{ font-size:15px; color:#fff;}
.button {display: inline;position: relative;font-size: 15px;font-weight: bold;text-align: center;text-decoration: none;color: white;border-radius: 5px;padding: 14px 80px;}
.bypass {margin: 20px;background-color: #333;text-shadow: 0 -1px -1px #1B3D82;}
.bypass:hover {background-color: rgb(6, 118, 146);box-shadow: rgba(255, 255, 255, .75) 0px 0px 9px 1px;}
</style>
<?php
echo '<center><br /><br />
<div class="head">Random Shit Bypasser</div> <br /> <br />
<form method="post">
<textarea name="urllist">'.htmlspecialchars($_POST['urllist'], ENT_QUOTES).'</textarea>
<br />
<input type=submit name="sub" class="button bypass" value="Bypass"/>
</form><br />';


if(isset($_POST['urllist']) && !empty($_POST['urllist'])){
    $array = array();
    $i = 1;
    $_POST['urllist'] = str_replace("\r", "", html_entity_decode($_POST['urllist']));
    $list = explode("\n", $_POST['urllist']);
    echo '<table border="1">';
    echo '<tr><th><font color="#fff">No .</font></th><th><font color="#fff">Link</font></th></tr>';
    foreach($list as $a)
    {
        if(empty($a)){
            continue;
        }

        else
        {
            $exp = get($a);
            if($exp === "ShitHappen1"){
                echo '<tr><th><font class="number">'.$i++.'</font></th><th>&nbsp;&nbsp;&nbsp;<font class="shittendstohappen">Can\'t bypass that link!</font>&nbsp;&nbsp;</th></tr>';
            }
            elseif($exp === "ShitHappen2"){
                echo '<tr><th><font class="number">'.$i++.'</font></th><th>&nbsp;&nbsp;&nbsp;<font class="shittendstohappen">Link provide is offline or not exist!</font>&nbsp;&nbsp;</th></tr>';
            }
            else {
                array_push($array, $exp);
                echo '<tr><th><font class="number">'.$i++.'</font></th><th>&nbsp;&nbsp;&nbsp;<a href="'.$exp.'"><font class="link">'.$exp.'</font></a>&nbsp;&nbsp;&nbsp;</th></tr>';}
            }
        }
        
          echo '</table>';
      
        # -- Count Random Shit Bypassed -- #
        if($CounT){
            $count = count($array);
            $handle = fopen('link.txt', "r");
            $num = fread($handle, filesize('link.txt'));
            fclose($handle);
            $numoflink = ($num + $count);
                        
            $handle = fopen('link.txt', "w");
            fwrite($handle, (int)$numoflink);
            fclose($handle);
        }

        # -- Count Random Shit Bypassed -- #
}

echo "<br /><br /><br />";
# -- Count Random Shit Bypassed -- #
if ($CounT) echo "<center><div class='foot'>Number Of SHIT Bypassed on ".$_SERVER["HTTP_HOST"]." is <b><u>".countLink()."</u></b></div></center>";

function countLink()
{
    if($handle = fopen('link.txt', "r"))
    {
        $realnumoflink = fread($handle, filesize('link.txt'));
        fclose($handle);
        return $realnumoflink;}

}
# -- Count Random Shit Bypassed -- #

function get($link){
        if(!preg_match('/^(http|https)/', $link)){
                $link = "http://".$link;
        }
        if(check($link)){
                $first = bypass($link);
                if($first !== false){
                        for($i = 0;$i<100;$i++){
                                $test = bypass($first);
                                if($test === false){
                                        break;
                                }else{
                                        $first = $test;
                                }
                        }
                        return $first;
                }else{
                        return "ShitHappen1";
                }
        }else{
                return "ShitHappen2";
        }
}

function bypass($link){
        $get = curl($link);
        if(strpos($get, "Location:")){
                preg_match_all('/Location: (.*?)/U', $get, $out);
                return $out[1][0];
        }elseif(preg_match('/(http:\/\/|https:\/\/\|)(www\.)?(q.gs|adf.ly)\/.*/', $link) ){
                preg_match_all('/var zzz \= \'(.*?)\'\;/', $get, $out);
                return $out[1][0];
        }elseif(preg_match('/(http:\/\/|https:\/\/|)(www\.)?.*\.(linkbucks.com|tinybucks.net)/', $link) ){
                preg_match_all('/Lbjs\.TargetUrl \= \'(.*?)\'/', $get, $out);
                return $out[1][0];
        }elseif(preg_match('/(http:\/\/|https:\/\/|)(www\.)?go\.urlcash\.net\/.*/', $link)){
                preg_match_all('/linkDestUrl \= \'(.*?)\'/', $get, $out);
                return $out[1][0];
        }elseif(preg_match('/(http:\/\/|https:\/\/|)(www\.)?lix\.in\/.*/', $link)){
                preg_match('/name=\'tiny\' value=\'(.*?)\'/', $get, $out);
                $data = curl($link, "tiny=".$out[1]."&submit=continue&submit=submit");
                preg_match('/src\=\"(.*?)\"/', $data, $out);
                return $out[1];
        }elseif(preg_match('/(http:\/\/|https:\/\/|)(www\.)?anonym\.to\/\?.*/', $link)){
                preg_match('/<p id=\"url\"><a href=\"(.*?)\"/', $get, $out);
                return $out[1];
        }elseif(preg_match('/(http|https):\/\/(www\.)?anonymz\.com\/.*/', $link)){
                preg_match('/<meta http-equiv=\"refresh\" content=\"0\; url=(.*)\">/', $get, $out);
                return $out[1];
        }elseif(preg_match('/(http|https):\/\/(www\.)?adfoc\.us\/.*/', $link)){
                preg_match('/[^\/\/]var click_url \= \"(.*?)\"\;/', $get, $out);
                return $out[1];
        }else{
                return false;
        }
}
 
function check($url){
        $ch=curl_init();
        curl_setopt($ch,CURLOPT_URL,$url );
        curl_setopt($ch,CURLOPT_RETURNTRANSFER, 1);
        curl_setopt($ch,CURLOPT_VERBOSE,false);
        curl_setopt($ch,CURLOPT_TIMEOUT, 1);
        curl_setopt($ch,CURLOPT_SSL_VERIFYPEER, FALSE);
        curl_setopt($ch,CURLOPT_SSLVERSION,3);
        curl_setopt($ch,CURLOPT_SSL_VERIFYHOST, FALSE);
        $page=curl_exec($ch);
        $httpcode = curl_getinfo($ch, CURLINFO_HTTP_CODE);
        curl_close($ch);
        if($httpcode>=200 && $httpcode<402) return true;
        else return false;
}
 
function curl($url, $post = ""){
        $ch = @curl_init();
        curl_setopt($ch, CURLOPT_URL, $url);
        curl_setopt($ch, CURLOPT_HEADER, 1);
        curl_setopt($ch, CURLOPT_USERAGENT, base64_decode('TW96aWxsYS81LjAgKFdpbmRvd3MgTlQgNi4xKSBBcHBsZVdlYktpdC81MzcuMjggKEtIVE1MLCBsaWt???lIEdlY2tvKSBDaHJvbWUvMjYuMC4xMzk3LjIgU2FmYXJpLzUzNy4yOA=='));
        curl_setopt($ch, CURLOPT_RETURNTRANSFER, 1);
        curl_setopt($ch, CURLOPT_SSL_VERIFYHOST, FALSE);
        curl_setopt($ch, CURLOPT_SSL_VERIFYPEER, FALSE);
        curl_setopt ($ch, CURLOPT_HTTPHEADER, array('Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8'));
        curl_setopt($ch, CURLOPT_TIMEOUT, 30);
        if($post){
                curl_setopt($ch, CURLOPT_POST, 1);
                curl_setopt($ch, CURLOPT_POSTFIELDS, $post);
        }
        curl_setopt($ch, CURLOPT_CONNECTTIMEOUT, 20);
        curl_setopt($ch, CURLOPT_FOLLOWLOCATION, 0);
        $page = curl_exec( $ch);
        curl_close($ch);
        return $page;
}
 ?>


so far
Supported : adf.ly,q.gs,linkbucks,tinybucks,urlcash,lix.in,anonym.to,goo.gl,anonymz.com,adfoc.us .

Sunday, February 3, 2013

How I spent my free day

Ever heard about BugCrowd?
Just knew about this recently. Thanks God I noticed from someone's tweet mentioning about this program.

BugCrowd - A Bug Bounty Program 

Do they offer any reward if we found any bugs in their website?
NO! They run managed bug bounties as their business. If there's any organisation want to do some testing on their websites, this guy will come around!

How the program works?
They will email the details when there's any website available for testing. A worth reward will be given as well!

How you can join this program?
Just register in their official blog here http://blog.bugcrowd.com/ and just need to wait for their updates!
Fyi, there's already Beta 004 mode. So, it still not too late to join the program :D

Did they really give you the reward?
:) Just joined their Beta 003 recently and...


For more, follow their updates from their twitter @bugcrowd


Friday, January 18, 2013

Wednesday, January 16, 2013

XSS in Google Art Project

Hi everyone.
This will be my 1st post for 2013. Hope it still not too late to wish you guys a Happy New Year. Hope you all live happily besides your love one :D

Few weeks ago, I found an XSS in one of the Google website, which is www.googleartprojects.com.
The vulnerable part found in the search box. Tested the inpur validation and checked the source page,

hmmmm???? Looks quite promising. Just testing my luck using a simple XSS payload

x”</title><img src%3dx onerror%3dalert(1)>

 and..

BOOM! its executed

My 1st XSS found in Google Inc!
Immediately made a POC report and submit it to google security team.

They received my report on Jan 7 2013.

And received this email early in the morning (different timezone -___-")
And, I'll be in the Google Hall of Fame in a next few days! Congratz to myself.

Then, I tried around to test more on it. And found that, there's a stored XSS as well in it!
BUT, unfortunately, because of my 1st report, my next report on the same website had been clarified as dupelicate -___-"


Days after submitted the report, I tried to google around about this website and found that there's already a report made by @NightRang3r (Mr Shai Rod) previously on this website. He found a stored XSS in it.


That's all.
Thanks
@yappare