Showing posts with label Hall of Fame. Show all posts

Tuesday, January 29, 2019

Sunday, April 24, 2016

Drag Drop XSS in Google ;)

Hi,

It was started with a tweet from Dr. Mario here https://twitter.com/0x6D6172696F/status/558346300790276096


Trying to understand the issue, I read on the comments and there's someone mentioned it is possible due to different format copied from OpenOffice such that. And Dr. Mario share his research on this and it is really interesting. http://www.slideshare.net/x00mario/copypest

Then, end of last year, noticed there's an XSS discovered by Harry in Google Docs using the drag drop technique. And due to improper validation HTML code read by Google Docs, the XSS can be executed http://hmgmakarovich.blogspot.my/2015/11/stored-xss-in-google-docs-bug-bounty.html 

I tried to look around Google Docs. Harry's submission did resolved, however, there's a module in Google Docs/Sheets/Drawing/Presentation where it allow a user to create a drawing. This module however does not fix yet.

Create a simple HTML file with our XSS payload, drag and drop into the drawing module, and the XSS is there :)

What make it interesting is that, I did take a look on the response given by the Google whenever a valid image or other different payload used. There were differ!

The drawing module was actually only looking for a valid image where it can come from user's computer or external source. If the source contain a valid image, the image then will be uploaded and properly embedded. If the image is broken, then it is broken. This is where the XSS payload below take in place.
<img src=nonvalid.jpg onerror=alert(0)>

This is because, the payload will execute if the source is broken (error). I tried using another payload such as onload,onmouseover etc, the XSS would not working! So here's a challenge. How we are going to make sure the image is loaded on victim's side, but once the victim drag into Google Docs, the image then will broken? Simple thought I used the valid image that exist in most of Windows users computer..yes..in C:\Users\Public\Pictures\Sample Pictures :)


 However! This submission was submitted by another researcher and this became a duplicate..but..

It was not in Google Images :)


Thanks!

Sunday, August 3, 2014

I hate you, so I pawn your Google Open Gallery

Hi, long time no see. Quite busy with works and probably will not able to update too much in future.

Going to share with you guys another bug I found in Google.
The bug as shown below.
Google is currently open service port 80 and 443. These ports are exposing what kind of service they're using. This bug worth $10k. Ok. Just a joke. Lets be serious.

Last time I found a bug in one of Google's service, Open Gallery. Using this service, it allows a user to share their exhibition art stuff (sorta) and each of the exhibition will be given a specific URL at *.culturalspot.org domain. And, this domain cannot be changed once we saved the name.

I created two different account for Open Gallery.
  1. jablor.culturalspot.org (using attacker@gmail.com) -
  2. test333.culturalspot.org (using prakhar's_motorbike@gmail.com)
Both of the current state for its exhibition page as shown below.
jablor.culturalspot.org

test333.culturalspot.org         
 I have some revenge at prakhar's_motorbike@gmail.com, and luckily this guy currently selling his arts using Open Gallery (test333.culturalspot.org). Lets pawn his Open Gallery!

What I'm doing below shows that
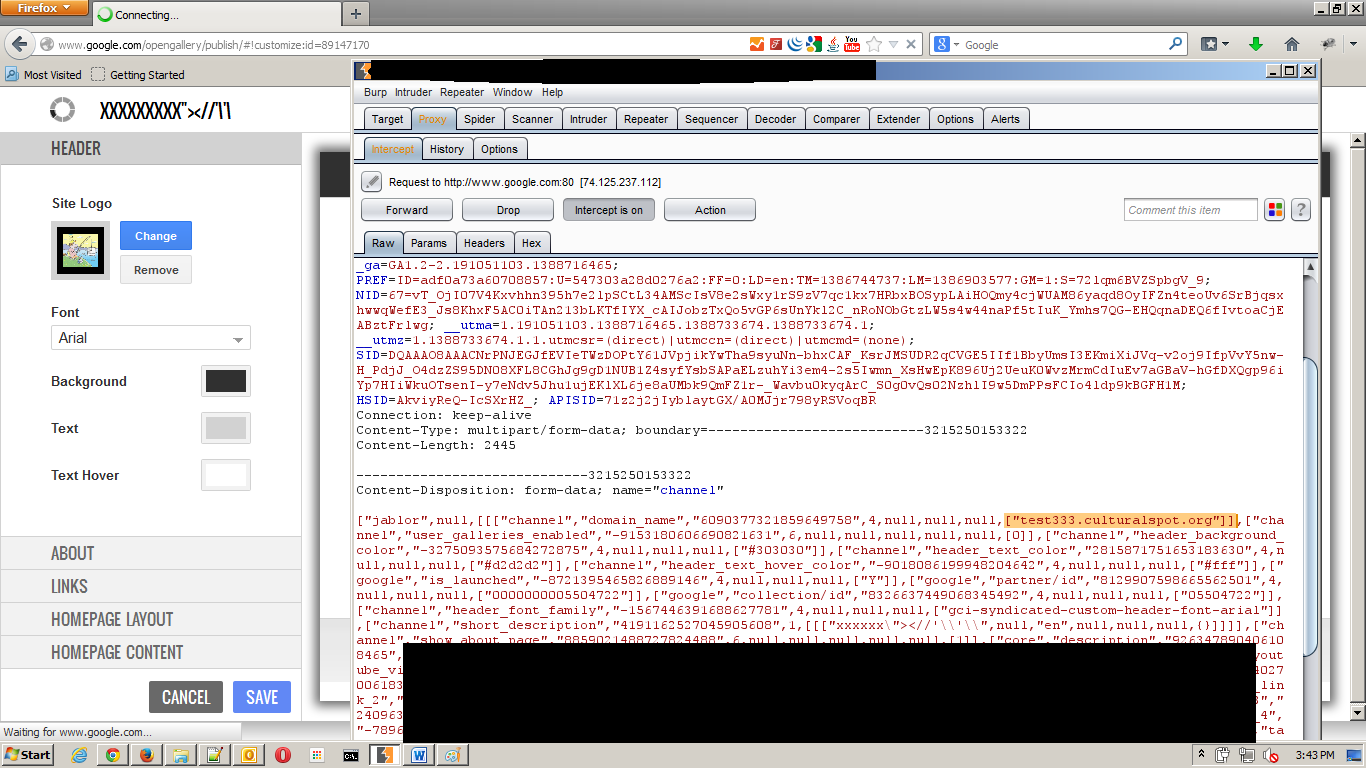
  1. I run up my Burpsuite in my account and try to save my current setting.
  2. I trapped the request during the saving process and change my domain from jablor.culturalspot.org into my target's URL, test333.culturalspot.org
  3. What happen? His Open Gallery stuff changed into mine and his domain owned by me. He will see his domain as my content and the content itself will be controlled by me. :)
Trigger up Burp and change the domain

My original culturalspot will be non-exist as its already changed into victim's URL
Victim's culturalspot with my content :)


That's all guys. Have fun.
This was fixed by Google Team :)

Sunday, February 2, 2014

Youtube - Stored XSS Strikes Back!

Hi,
Remember above picture? Most of you might thought its an XSS vulnerability in Gmail, sad to say it is not.haha..The bug actually exist in Youtube Api. Yes, similar to my previous post Yay the Nay in Youtube, this bug also came from the same Youtube Api.

The vulnerable parameter was track's name. Interesting part is, if you try to use XSS payload directly as track's name, it won't working. An error will appear saying you're trying to use special characters that are not allowed.

But due a glitch occur in this section, I was able to change the track's name by using "edit" function. By directly replay the request or tamper it, I can change the old_name into a new name with my XSS payload as shown below.


Once saved, the XSS successfully stored in my video. So does it mean if you watch the video from www.youtube.com it'll executed? Sadly, no. However, the XSS can be executed in Gmail, Google Docs/Presentation and Google Plus. This is because the video will be played using Google's player that was affected with this vulnerability.


Simple right?
Till next time,adios!

@yappare

10 January 2013 : Reported to Google
11 January 2013 : Received notification from Aleksandr, Google Security Team
12-14 January 2013 : Bug noticed was fixed around this date.
15 January 2013 : Received email regarding reward
22 January 2013 : Confirmation of fix from Google's team.


#edit: Prakhar my friend said that this XSS actually execute on youtube main domain as well since he was double check for me on that day and it work in www.youtube.com. sadly I dont have the screenshot as a proof

Tuesday, January 14, 2014

Again, from Nay to Yay in Google Vulnerability Reward Program!

Happy new year to everyone. This is my first post for 2014.

On 9th January 2014, I posted this on my twitter
https://twitter.com/yappare/status/421470672330571777/photo/1
So is this post related to that? Will get to it soon or probably next month.haha..
In this post I'm going to share to you a bug that manage me to be inside  Google Vulnerability Reward Program G+ Community here

The bug is a Self Stored XSS in Youtube. Yerp..

Let us see how the XSS exist.
  1. In Youtube video manager, there's a function for a user to create Captions for his/her video(s).
  2. Put our XSS payload in the script box and save.
  3. Once we play the video, our XSS will be executed.
  4. Check on below screenshots :)


But..there's a problem! The XSS only executing in Caption's Video Manager. Which in other word the XSS is only stored for that user only.
Hmmm...
There's must be a way to exploit or to manipulate this vulnerability. Last time I managed to find a way to Yaying this Nay in Google Adwords. You guys can check on it http://c0rni3sm.blogspot.com/2013/12/google-adwords-stored-xss-from-nay-to.html

I browsed a few times to see is there any share or embed function in this Captions thing. And then..


I noticed that, there's a function where a user can request for a translation from 3rd party or other users. So how this function working?
  1. User request for his/her video for a translation.
  2. User able to choose either from 3rd party or by other Google Users.


Manipulating time.Let assume that, there's a community for English series, Movies, Korean dramas that have some translator for Youtube's caption..and among them, there's an attacker >: )
  1. Attacker will received the invitation.
  2. Attacker put his/her evil code in the middle of translations.
  3. Send to the requester for approval.


Once done, the requester will get an email notification and what she/he need to do is review the translated caption and approve it. So what happen next? The XSS will be executed 


and


Till next time, adios!

@yappare


03 December 2013 - Reported via VRP form
07 December 2013 - Received a reply from Martin,Google Security Team
07 December 2013 - Google Team asked for more information to reproduce
08-10 December 2013 - Fixed around these dates.
11 December 2013 - Received a reward email from Google
10 January 2014 - Kevin,Google Security Team confirmed the fix.

Sunday, December 15, 2013

Google Adwords Stored XSS - From Nay to Yay!

Hi,
This is an old issue that I submitted to Google previously. Already shared the POC at my twitter on Sep' 13.


I promised to share a writeup on my recent finding in Google, but since the security team going to take some time to fix them, I'll share this as a replacement.

This issue was fixed in 2-3 days after my submission date. This is quite an interesting finding actually. The bug exist in the uploader function at "Upload editable report" under "Reports and uploads" tab.

A user can upload a report through this uploader for his/her reference in future. However, the filename parameter for the file can be manipulated since there's no sanitization happen on it.

The only filetype allowed to be uploaded are excel type; csv and tsv as shown in the website.
So what I did was, run a Burp to intercept the request and then change the filename into XSS payload.


Awesome!!!! A STORED XSS!! Moreover, if you guys look on it closely, the payload is properly hidden from user's view. Nice eh? haha..
Sent the report to Google team, and then wait for a few days to get their receive. At first I wonder why they took quite some times to accept this issue. Then, I realize that...this is actually...a SELF STORED XSS!!!


The team might reject or reward me with less amount if this is the case!!


But..


Thanks to Nirgoldshlager presentation in Blackhat 2012 about his bounties I have my mind what I need to do.

As you can see, there's a function in Adwords where the owner of the account can invite his/her friend as a partner! Let us see if it working :)


yup2..our victim take his/her action to be a partner of evil mind.muahahaha..a confirmation email will be sent to us and we just need to grant the access to the victim.


Done. And the victim will get the confirmation email and then happily login into his/her Adwords account..

and....
Sorry partner.muahahahaha...

Google Team response, 
 

So, I'm actually lucky since Adwords have this kind of function..but what if there's none?!!! This guy might have the answer :)


Thanks for your time. :)

Cio.